1/11 The shenanigans described in the Anthropic report are incredible.
A 🧵👇🏻
@JamieMetzl @niubi @Byron_Wan #DRASTIC
2/11 GTG-10007: Exploit foundries and autonomous attack frameworks
We identified and investigated a sustained espionage operation, tracked as GTG-10007, conducted by Chinese-speaking operators likely residing in Changsha in China’s Hunan province.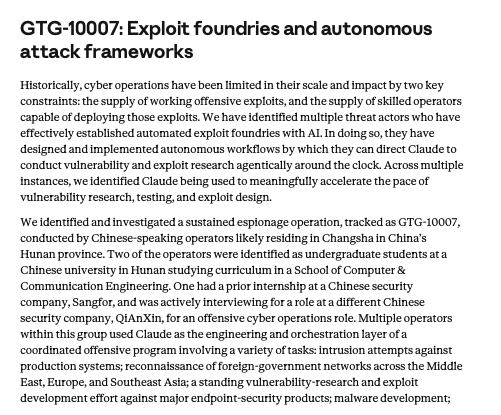
3/11 GTG-14010: Disrupting a China-based surveillance and recruitment operation targeting Uyghurs in Syria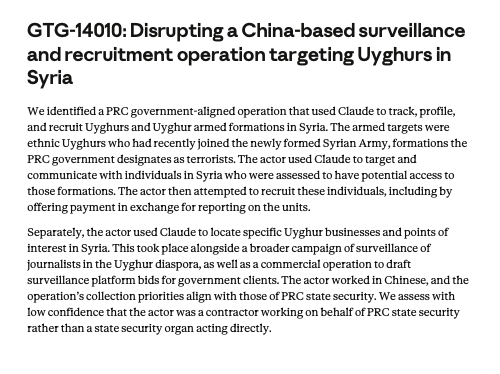
4/11 GTG-14020: Disrupting a China-based religious affairs intelligence operation targeting Catholic, Tibetan Buddhist, Falun Gong, and Taiwanese Christian communities.
In one case, a user disclosed that they were an information security officer for the Chinese state.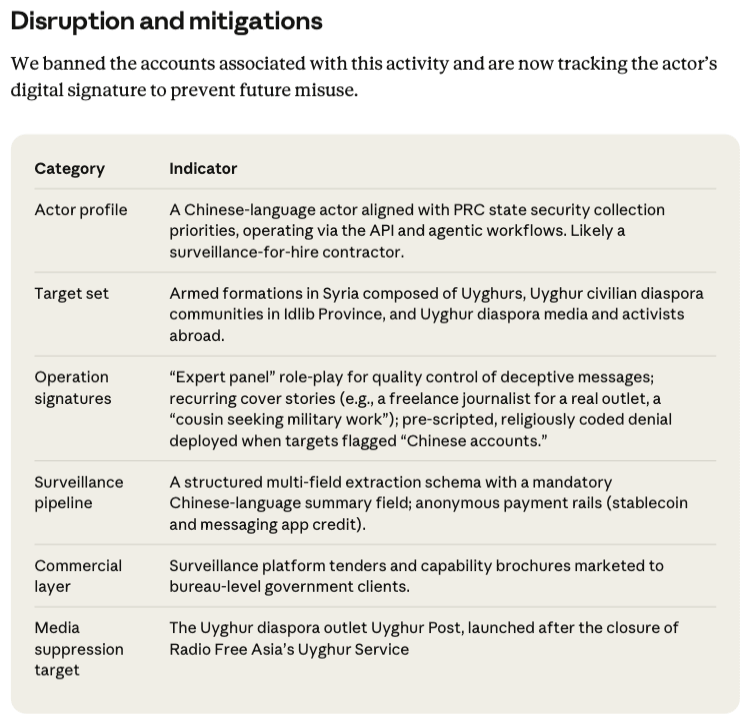
5/11 GTG-14021: Disrupting a China-based public and state security campaign of “stability maintenance” surveillance and transnational repression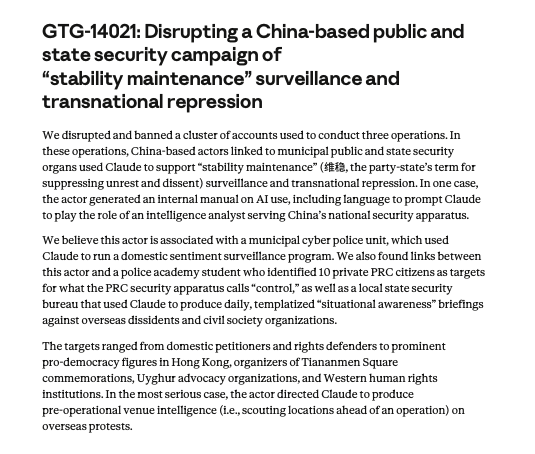
6/11 GTG-14022: Disrupting a China-based “public opinion monitoring” and dissident surveillance operation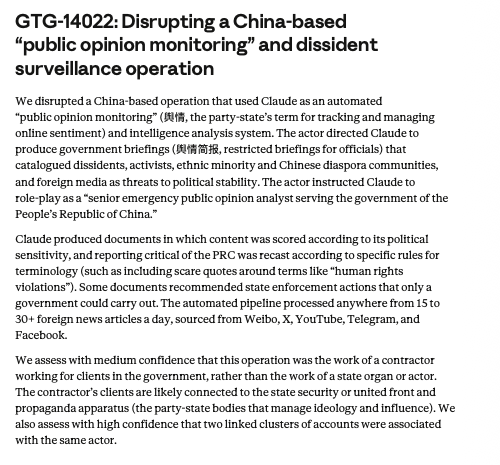
7/11 GTG-16001/2: DeepSeek/Moonshot serves Claude instead of its own models and collects exchanges for model training
🤷♂️Requests included:
• PLA-affiliated surveillance activity.
• An engineer at a major PRC SOE, who revealed internal code and live credentials from multiple major PRC companies!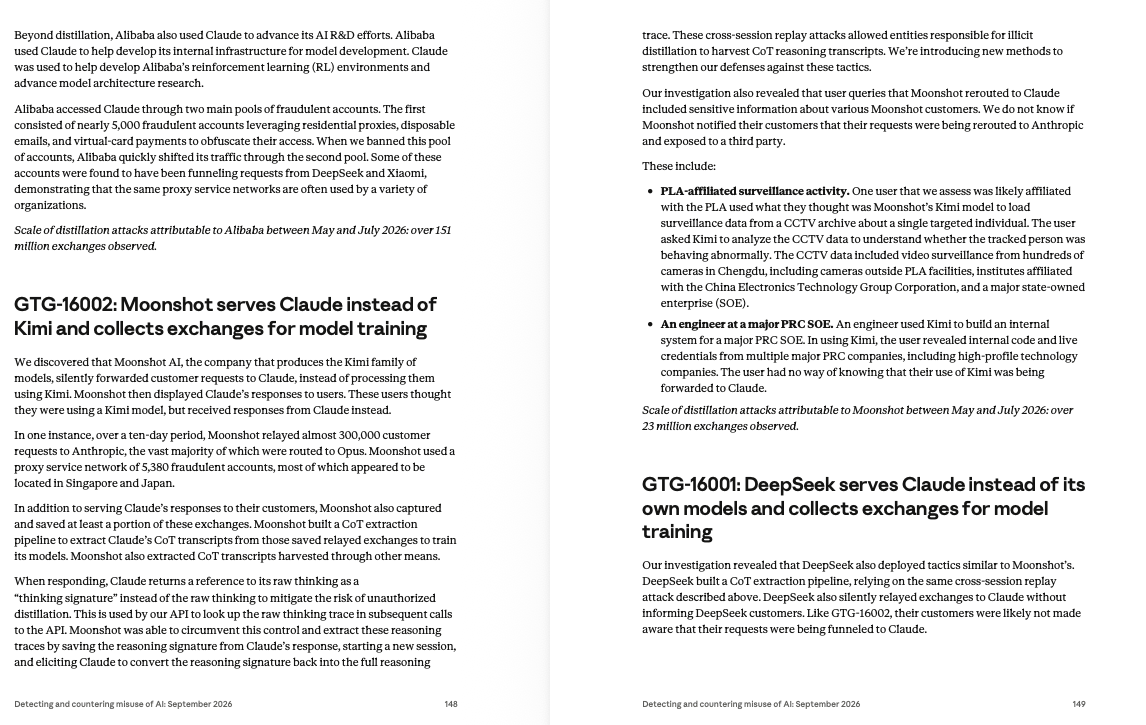
8/11 GTG-17002: Disrupting a China-based operation using Claude to build targeting software for electronic warfare and air defense suppression
One user likely affiliated with the PLA loaded surveillance data from a CCTV archive about a single targeted individual.
9/11 The user asked Kimi to analyze the CCTV data to understand whether the tracked person was behaving abnormally. The CCTV data included video surveillance from hundreds of cameras in Chengdu, including cameras outside PLA facilities.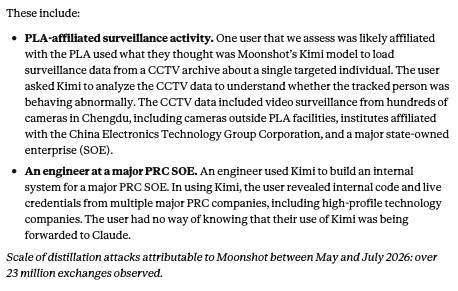
10/11 And you also have all the usual GoF and DURC research requests from dubious countries (China, Russia or Iran most likely).
See previous thread.
x.com/gdemaneuf/status/2098186381172543499

Gilles Demaneuf
@gdemaneuf
Pointy Head. Opinions, analyses and views expressed are purely mine and should not in any way be characterised as representing any institution or company.